A Amol Ghuge Résumé

Open to senior engineering roles

I build products that hold up
in production — not just in demos.

Senior Full-Stack Engineer with 6+ years across the full lifecycle: web frontends, cross-platform mobile, API design, cloud infrastructure and application security. I've taken greenfield products from an empty repo to 10,000+ users at 99.9% uptime.

Based in
Pune, India · IST
Currently
Globant
Focus
Full-stack · Mobile · APIs
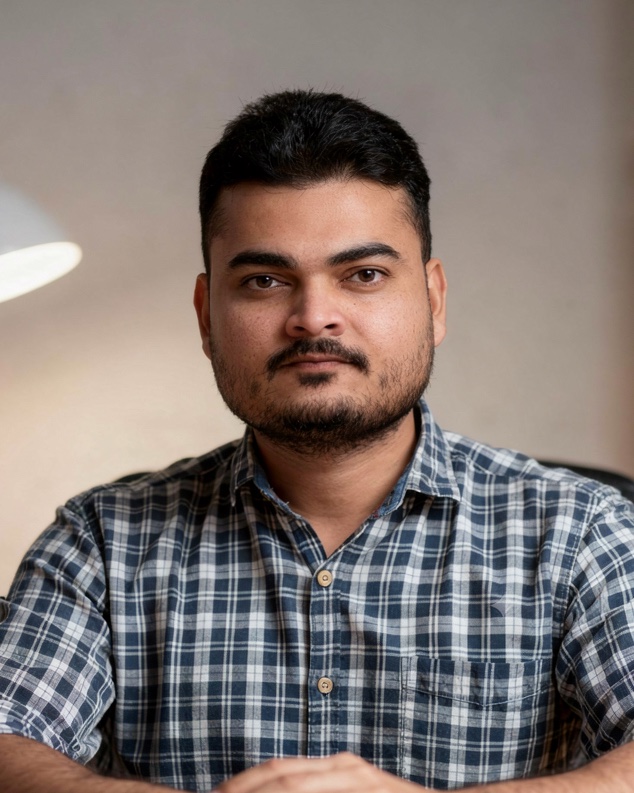
Portrait of Amol Ghuge
Amol Ghuge Senior Full-Stack Engineer · Pune, IN
50+ Banking clients served by the payment API I built
25% Fewer regression incidents after my test suite
60% Manual data entry eliminated at client onboarding
15+ Hours of manual QA effort saved every week

01 Case studies

Selected engineering work, with the reasoning behind it

Client work under NDA, so these describe the problem, the approach and the measured outcome.

Case 01

Greenfield product, zero to 10,000 users

Globant · 2024 – present

Problem
A new product needed to exist in weeks, not quarters — with enterprise auth, audit-ready access control and no tolerance for downtime once customers arrived.
Approach
I designed the whole stack: a Next.js frontend, an Express service layer with validated request boundaries, and normalised PostgreSQL schemas via Prisma. Auth went through Okta (OAuth 2.0) with role-based access enforced server-side rather than in the UI. Deployments ran on Vercel behind environment-scoped configuration and secrets.
Outcome
10,000+ users at 99.9% uptime, zero unauthorised-access incidents post-launch, and a codebase two other teams later built on without a rewrite.
  • Next.js
  • Express
  • PostgreSQL
  • Prisma
  • Okta
  • RBAC
  • Vercel

Case 02

Micro-frontends to unblock parallel teams

Globant · 2024 – present

Problem
Multiple product teams shipped from one frontend codebase. Every release became a coordination meeting, and one team's regression blocked everyone else's deploy.
Approach
I split the app into independently deployable micro-frontends with explicit contracts at the boundaries, then tuned the Webpack build with code splitting and lazy loading so the composition didn't cost users anything. Shared design primitives lived in one versioned place to stop the UI from drifting apart.
Outcome
Release conflicts eliminated, delivery velocity up, and faster initial page loads with improved Lighthouse scores despite a larger overall application.
  • Micro-frontends
  • Webpack
  • Code splitting
  • Design system
  • CI/CD

Case 03

Real-time payment API for 50+ banks

Accenture · 2022 – 2024

Problem
Banking clients needed real-time payment processing. Latency was a commercial issue — slow transactions cost deals.
Approach
I engineered the API on Java Spring Boot with careful attention to the transaction path: connection handling, validation placed before expensive work, and failure modes that degraded safely rather than leaving payments in limbo.
Outcome
Served 50+ banking clients with reduced transaction times, and the capability became part of the pitch that won new business.
  • Java Spring Boot
  • REST
  • Payments
  • Concurrency

Case 04

High-volume quoting and document services

Accenture · 2022 – 2024

Problem
Underwriters needed hundreds of simultaneous insurance quotes, and compliance teams were manually converting and virus-checking thousands of documents a day.
Approach
For quoting, I dispatched concurrent requests through the Guidewire Edge API with bounded parallelism and per-request error recovery so one failure didn't sink a batch. For documents, I built Node.js conversion and virus-scanning microservices, plus a React + PSPDFKit editor for page-level manipulation. An Excel-to-JSON converter removed the worst of the manual onboarding work.
Outcome
Thousands of documents processed daily without manual handling, and manual data entry cut by 60% during onboarding.
  • Guidewire Edge API
  • Node.js
  • React
  • PSPDFKit
  • Microservices

Case 05

Closing injection-class vulnerabilities

Infosys · 2019 – 2022

Problem
A platform handling live enterprise data had grown without an adversarial review. User input reached SQL statements, shell commands and the filesystem through paths nobody had traced.
Approach
I audited the request paths end to end and fixed each vulnerability class at its source rather than filtering symptoms: parameterised every dynamic query, validated and allow-listed input before it could reach a shell command, and resolved-then-verified file paths so traversal outside the intended directory became impossible. In the same pass I reworked MySQL schema design and indexing and moved search, filtering and pagination server-side.
Outcome
SQL injection, OS command injection and path traversal closed across the application, with materially improved response times on the high-read paths.
  • Security auditing
  • Java Spring Boot
  • MySQL
  • Query optimisation
  • Input validation

04 Experience

Six years, three enterprises, one throughline

The depth is in the case studies above — this is the shape of the career and what each role added.

  1. Globant

    – Present

    Pune, India

    Senior Full-Stack Engineer

    Lead engineer on a greenfield product: designed both the Next.js frontend and the Node.js service layer, then owned it through launch and scale.

    • Built the unit and integration suite in Jest + React Testing Library, reducing regression incidents by 25%.
    • Owned CI/CD and Vercel deployments, including environment-scoped configuration and secret management across staging and production.

    Detailed in cases 01 & 02 ↑

    • Next.js
    • React
    • Node.js
    • Express
    • PostgreSQL
    • Prisma
    • Okta / OAuth 2.0
    • Micro-frontends
    • Vercel
    • Jest
  2. Accenture

    –

    Pune, India

    Senior Full-Stack Developer

    Insurance and banking delivery — payment rails, high-concurrency quoting, and document tooling used daily by internal compliance teams.

    • Delivered 5+ insurance products end to end with React and Guidewire Jutro, owning API integration, business logic and cross-browser behaviour.
    • Cut hand-written boilerplate 70% on the Jutro Digital Platform and halved UI delivery time with Storybook and Figma-to-code workflows.

    Detailed in cases 03 & 04 ↑

    • React
    • Guidewire Jutro
    • Java Spring Boot
    • Node.js
    • PSPDFKit
    • Microservices
    • Storybook
    • Figma
  3. Infosys

    –

    Pune, India

    Senior System Engineer — Full-Stack

    Enterprise integration and platform hardening, plus a travel booking product I owned from schema design through deployment.

    • Integrated two major enterprise platforms through Java Spring Boot microservices, improving interoperability and reducing API latency.
    • Designed and built a full-stack travel booking platform (Spring Boot, React, MySQL), owning the product lifecycle end to end.
    • Wrote a Java test-data generator that saved 15+ hours of manual effort weekly and unblocked the QA pipeline.

    Detailed in case 05 ↑

    • Java Spring Boot
    • React
    • MySQL
    • Microservices
    • Security auditing
    • Query optimisation

05 Tech stack

The toolkit, honestly labelled

Everything here has shipped to production in the work above — grouped by what it does, not by how impressive it sounds.

Languages & runtime

  • TypeScript
  • JavaScript
  • Node.js
  • Java (Spring Boot)
  • Python
  • SQL
  • HTML5 & CSS3

Frontend & mobile

  • React.js
  • Next.js 15
  • React Native & Expo
  • Redux
  • TailwindCSS
  • Storybook
  • Micro-frontends
  • Guidewire Jutro
  • App Store & Play Store releases

Backend & APIs

  • Express.js
  • REST & GraphQL
  • Microservices
  • Edge APIs
  • Rate limiting
  • Validation & error handling
  • Guidewire Edge API

Data

  • PostgreSQL
  • MySQL
  • MongoDB
  • Prisma ORM
  • Redis
  • Schema design
  • Indexing & query optimisation

Cloud & DevOps

  • AWS EC2, S3, Lambda
  • Docker
  • GitHub Actions
  • CI/CD pipelines
  • Vercel
  • Git

Architecture & security

  • Micro-frontend (MFE)
  • OAuth 2.0 (Okta)
  • RBAC
  • SQL & OS injection defence
  • XSS mitigation
  • Path traversal fixes
  • Webpack & Metro tuning

Testing & craft

  • Jest
  • React Testing Library
  • Integration testing
  • Postman
  • Figma-to-code
  • Code review
  • JIRA

Currently learning

  • Applied ML fundamentals
  • Transformer internals
  • Model Context Protocol
  • Voice AI pipelines

06 About

An engineer who owns the whole slice

I started as a self-taught programmer and have spent the last six years in enterprise engineering teams — the kind where a bad deploy shows up in someone's bank statement. That shaped how I work: design for failure first, then make it fast.

Today I architect greenfield products end to end. That means schema design and normalised data models, REST APIs with validation and rate limiting, React and Next.js frontends split into independently deployable micro-frontends, React Native apps shipped through the App Store and Play Store, and the CI/CD that carries all of it to production.

I care about the parts nobody demos: auth boundaries, RBAC, injection surfaces, query plans under concurrent load, bundle budgets, and test suites that actually catch regressions.

I work well with product and design — I've cut UI delivery time in half using Storybook and Figma-to-code workflows, and I'd rather ask one clarifying question early than rebuild a feature twice.

Outside of shipping, I write a long-form series taking machine learning apart from first principles — tokenisation, embeddings, attention, the KV cache. Explaining a system plainly is the fastest way to find out whether you actually understand it.

How I work

  1. 01

    Own the whole slice

    A feature isn't done at the API boundary. I take responsibility from the data model through the UI to the deploy, because that's where the real bugs live — in the seams between layers.

  2. 02

    Design for failure first

    Validation at the edge, centralised error handling, rate limits, and recovery paths for partial failure. Systems that degrade gracefully beat systems that are fast until they aren't.

  3. 03

    Security isn't a phase

    Access control is enforced server-side, never in the UI. I've audited and patched injection and traversal classes of bugs, and I'd rather find them myself than read about them in an incident report.

  4. 04

    Measure, then optimise

    Query plans, bundle sizes, Lighthouse scores, regression counts. I change what I can measure and leave the rest alone — premature optimisation is just complexity with better PR.

07 Contact

Let's talk about what you're building.

I'm open to senior full-stack, backend and mobile roles, and to selective freelance work. If you're hiring, tell me about the product and the problem — I'll tell you honestly whether I'm the right person for it. I reply within a day.

100xdev.amol@gmail.com